From senior engineer to agent orchestrator
Why senior engineers should move beyond faster coding and design human-agent systems with permissions, verification and clear ownership.
Senior engineers do not need another argument for using AI. Most already use it for code, tests, documentation, incident notes or research. The harder career question is how to become the person who can put agents inside real engineering work without weakening production safety.
Microsoft's 2025 Work Trend Index uses the phrase agent boss for a worker who builds, delegates to and manages agents. The title matters less than the operating responsibility behind it: someone has to decide what the agent can see, what it can change, who reviews the output and how the team recovers when it is wrong.
The new senior signal
A mid-level engineer can ask a model to generate a migration or a pull request summary. A senior engineer has to notice the missing boundary: the database role is too broad, the rollback path is vague, the test only covers the happy path, or the deployment step assumes a secret that should never enter a prompt.
That judgment matters more as agents get access to tools. Tool access turns a chatbot into an actor inside the workflow. The agent may read logs, open tickets, inspect pull requests, run checks, draft a remediation plan or prepare a transaction bundle. Each useful capability also creates a permission problem.
What orchestrators design
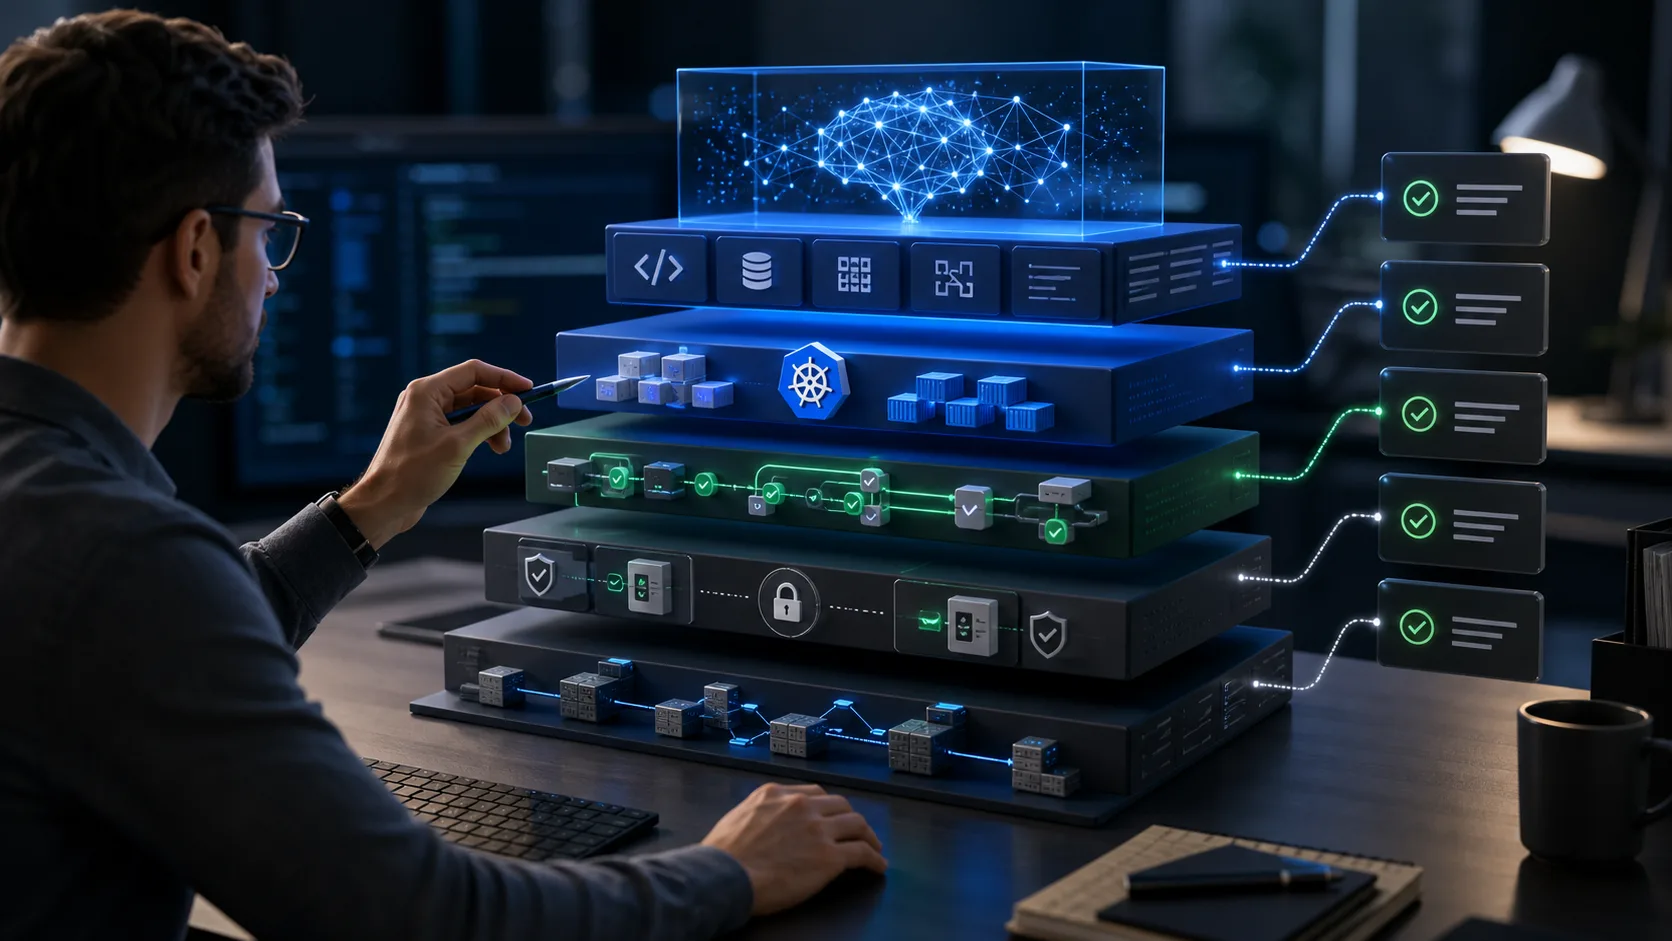
- Context rules: which repositories, logs, tickets and runbooks the agent can use.
- Tool boundaries: separate read-only inspection from write, deploy or transaction-preparation actions.
- Approval gates: define which actions need a named human before execution.
- Verification paths: require tests, simulations, static checks or reviewer evidence before high-risk changes.
- Audit trails: record inputs, tool calls, outputs, approvals, failures and rollback decisions.
- Secret handling: keep credentials, wallets, API keys and production config out of prompts and model-visible context.
The real work is control design
Delegating to an agent is easy when the task is reversible. The work gets serious when the agent can touch systems that affect customers, money, availability or security posture. At that point, the design question is not whether the model can produce a plausible answer. It is whether the surrounding workflow can keep a bad answer from becoming an action.
A useful agent brief reads like an operating contract. It names the actor, the permitted evidence, the blocked actions, the approval rule, the check that must pass and the fallback when the agent cannot prove its result. If the brief cannot say those things, the agent should stay in advisory mode.
- Before giving write access, prove the read-only workflow produces useful evidence.
- Before automating execution, prove human approval is fast enough and recorded.
- Before trusting summaries, compare them against logs, diffs or metrics the agent did not generate.
- Before adding another tool, decide which failure mode it introduces.
Why infrastructure engineers have an edge
Backend, DevOps, security and blockchain engineers already work with the constraints agentic systems need. They know service contracts, identity, queues, CI/CD, observability, incident response, signing flows, multisig approvals, RPC reliability and irreversible execution. Those constraints are not side details. They are the architecture.
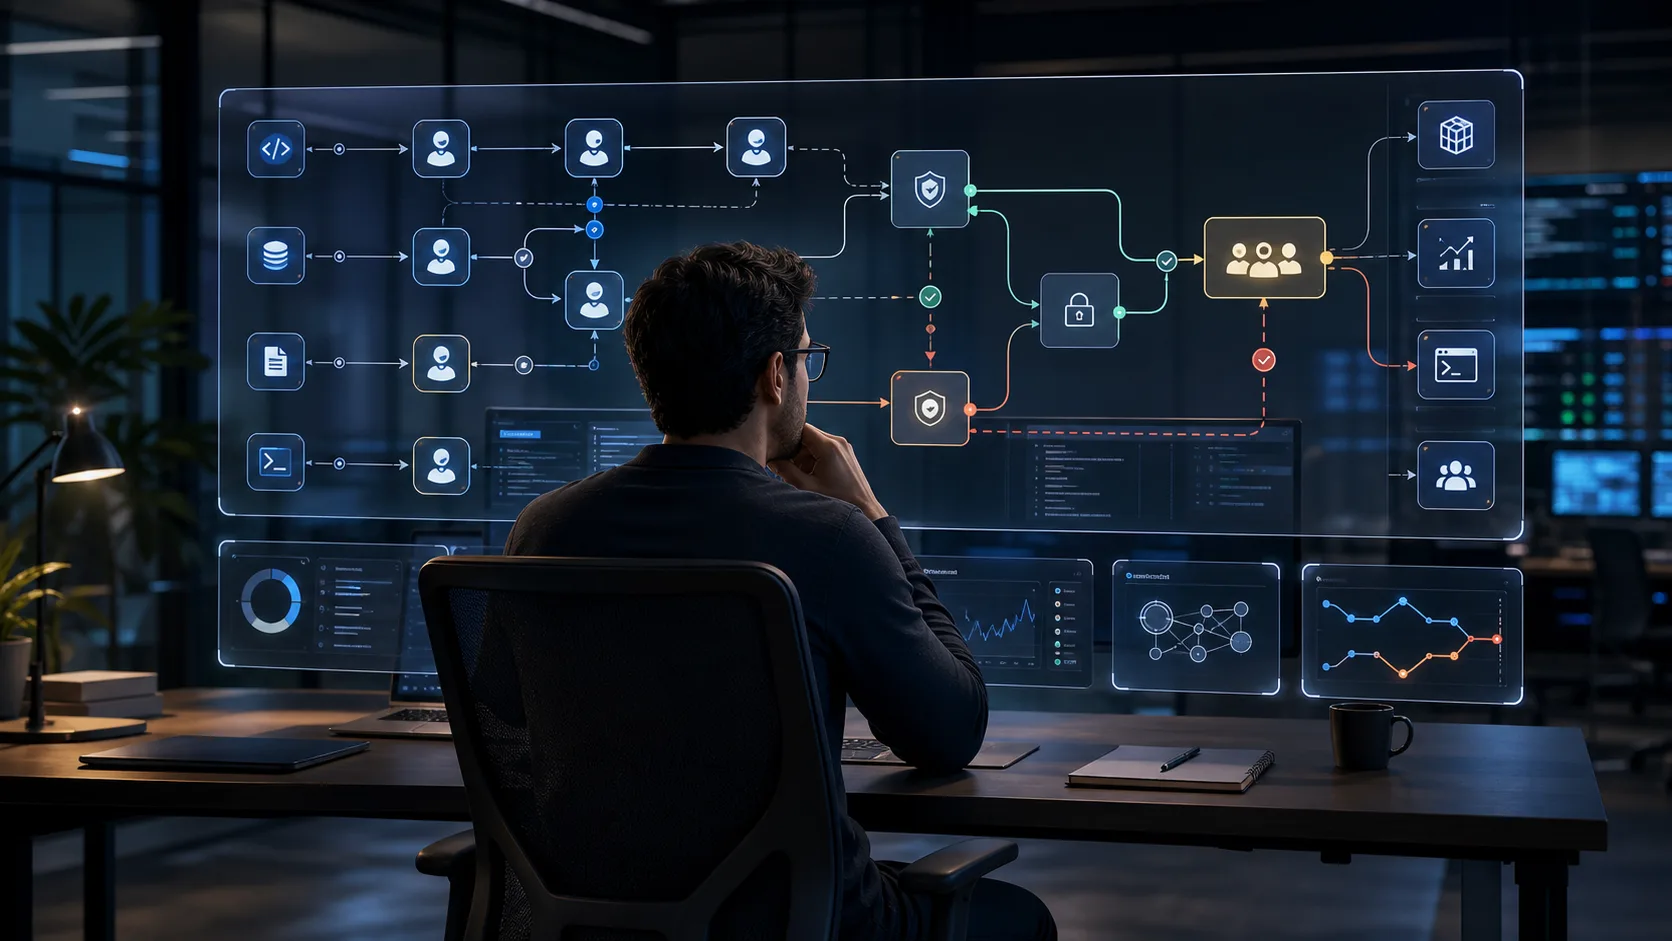
A practical example is a deployment investigation agent. It can compare recent commits, inspect Kubernetes events, check RPC health, read the release runbook and draft a rollback plan. It should not restart production services or submit a Safe transaction without human approval. It should fail closed, keep evidence and explain the risk in terms the accountable engineer can review.
This is where the senior role changes. The engineer is no longer only reviewing code after the model writes it. The engineer is designing the path that decides what evidence enters the model, which output leaves it, which checks run automatically and which decision stays with a named person.
Career move
Position yourself as the engineer who can redesign engineering work so agents do useful work under control. That means you can write the code, define the boundaries, build the checks and explain why the workflow is safe enough to run.
A strong personal artifact is an agent production-readiness checklist: access, tool scope, verification, approval, logging, rollback and owner.
Further reading
Nexuain practical implication
Agents should expand a senior engineer's judgment, not bypass it. That means explicit context boundaries, tool permissions, approval gates, and audit trails before agent work touches production systems.
Internal links
Source registry
Need help applying this to your launch or workflow?
Request a technical review and we will map the safest first step.