AI Agent Security Automation
AI agents with guardrails, approvals and audit trails
Design AI agent workflows that can help with real work while staying scoped, logged, and reviewable.
Request a technical review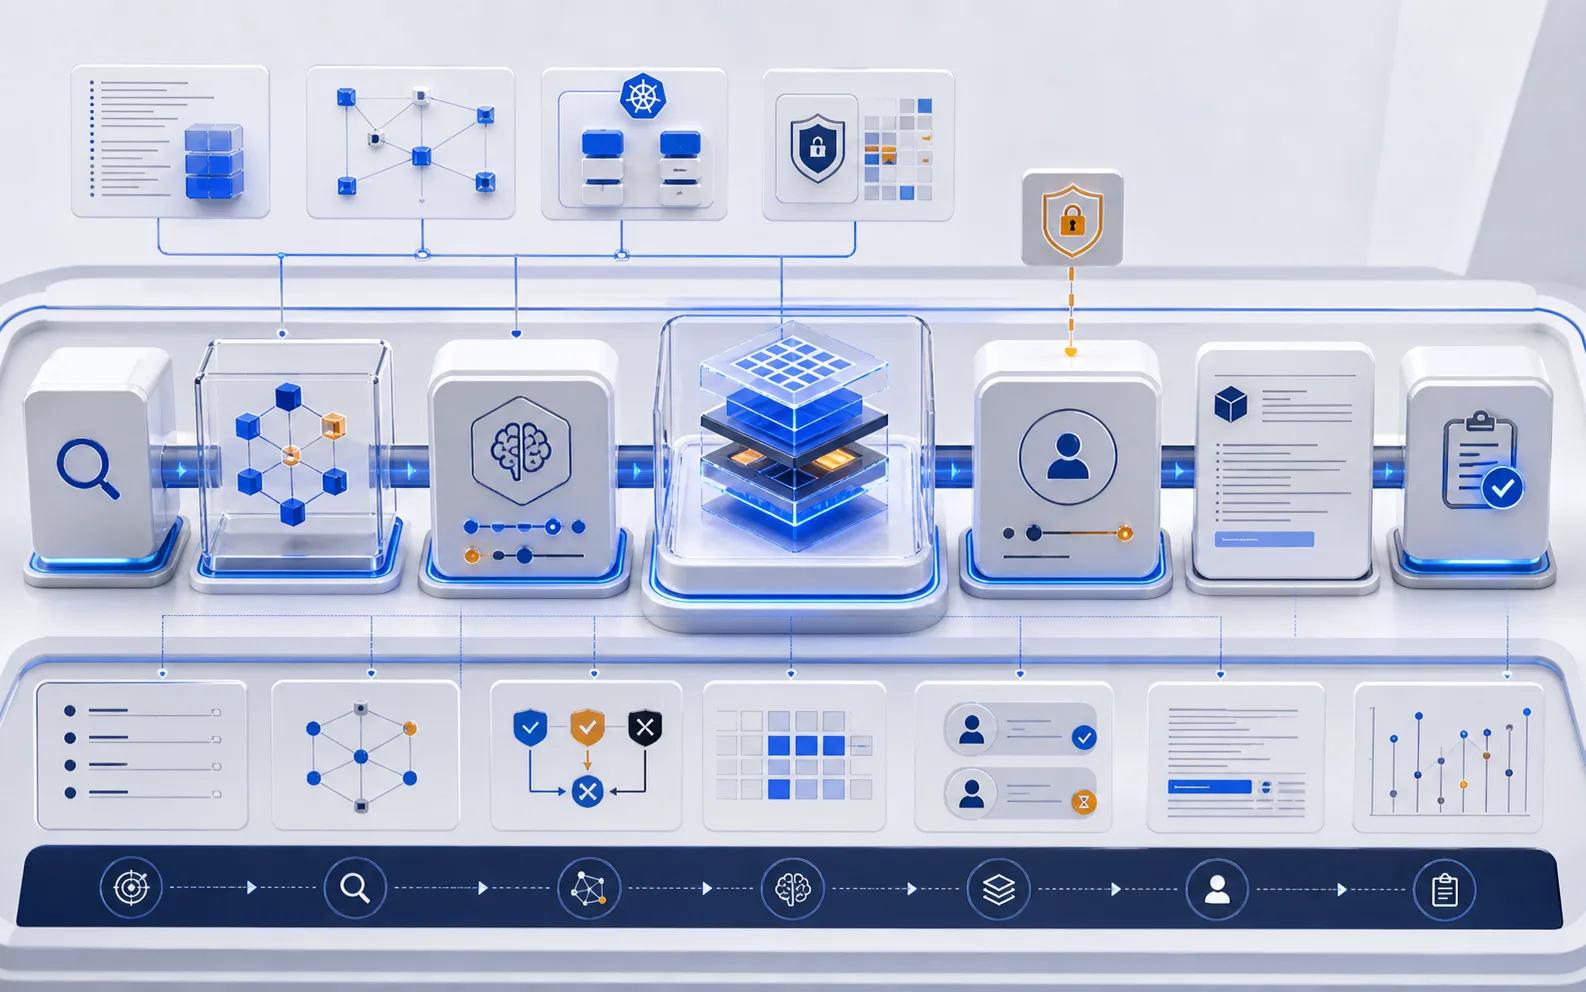
Service overview
- Pain
- Agents become risky when tools, data access, permissions, and human review are not explicit.
- What we build or review
- We map failure modes, tool scopes, approval gates, logs, and review loops for practical AI workflows.
- Who it is for
- Technical teams adding agents to operations, support, research, reporting, or internal workflows.
The painful problems
- • Unclear tool permissions
- • No approval gate before sensitive actions
- • Weak audit trail
- • Agents exposed to unnecessary data
What Nexuain designs
- • Scoped tools and permissions
- • Human-in-the-loop checkpoints
- • Prompt and context boundaries
- • Logging and operational review
Deliverables
- • Workflow design
- • Guardrail checklist
- • Prototype path
- • Handover documentation
Important boundary
Critical business or blockchain actions must remain explicitly approved by accountable humans. Default scope excludes high-risk Annex III uses unless separately reviewed.
Design and implementation support for controlled AI agent workflows. Not an EU AI Act conformity assessment, CE marking, or certification. Provider/deployer roles and transparency duties are allocated per project. Critical actions require explicit human authorization. High-risk Annex III uses (for example hiring decisions, credit scoring of natural persons, biometric emotion recognition, law-enforcement decisioning) require separate legal review and are out of default scope.