Safe multisig operations: from manual approvals to auditable runbooks
How Web3 teams can improve Safe and multisig operations with owners, transaction context, approval checklists and emergency runbooks.
A multisig is only as strong as the workflow around it. Safe can enforce signatures, but it does not automatically explain transaction intent, verify reviewer context, preserve evidence, or rehearse emergency decisions.
Problem
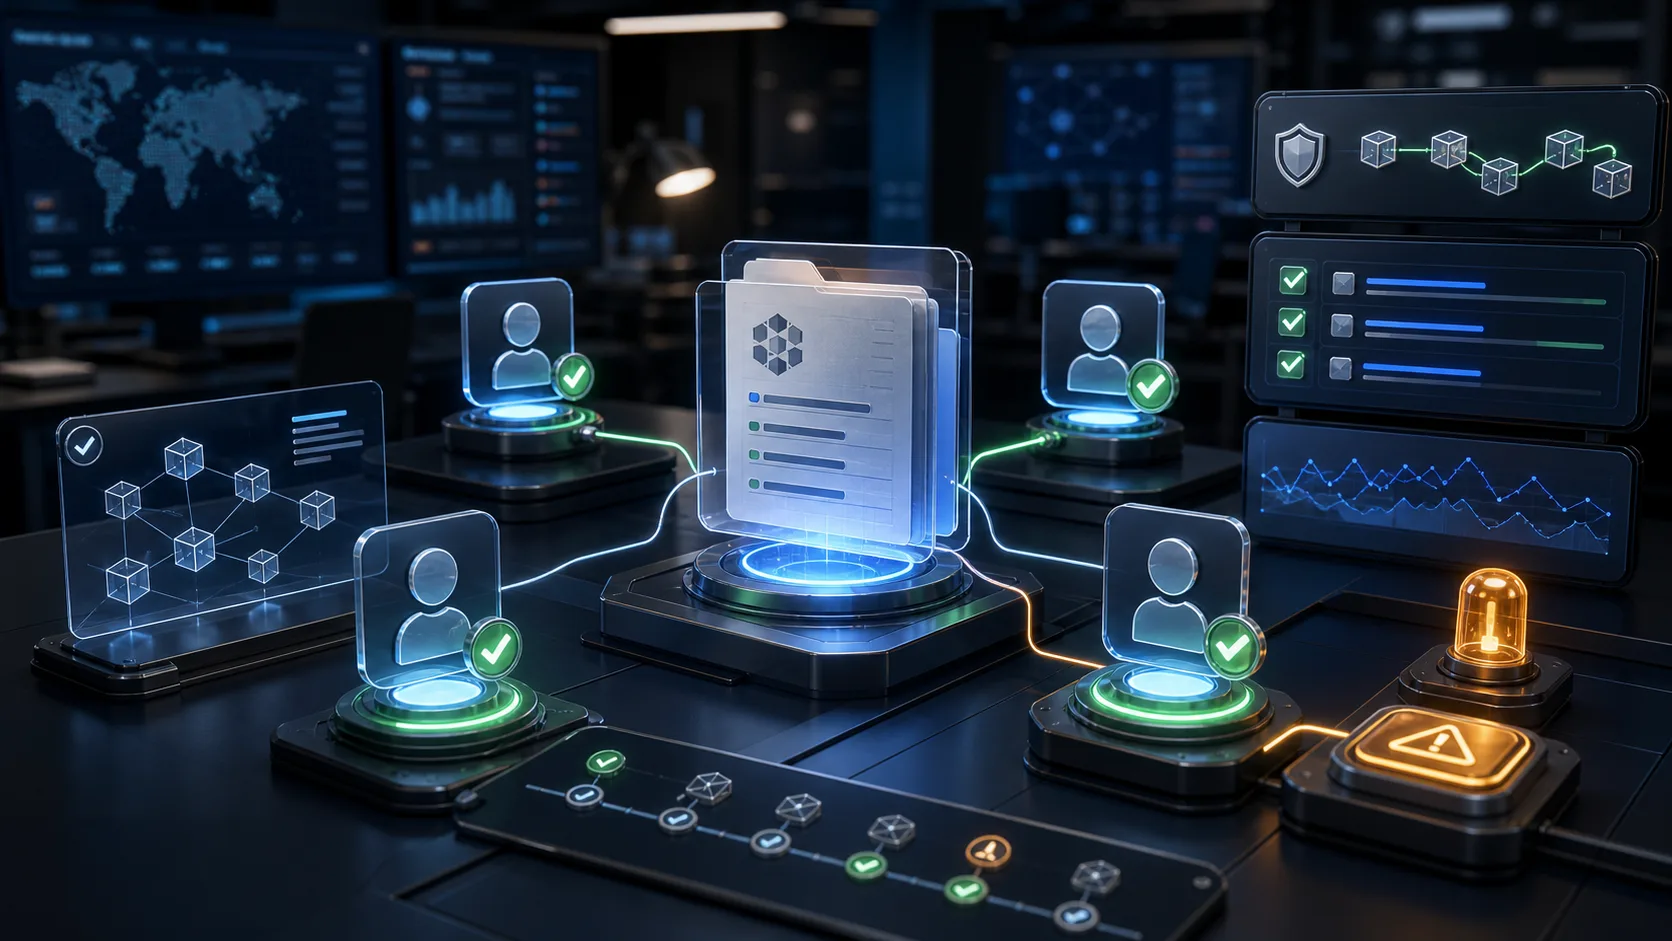
Many teams prepare transactions in one place, discuss them in another, approve them in Safe, and later struggle to reconstruct why a decision happened. That may work for routine changes, but it is brittle during launches, incidents and treasury operations.
Practical checklist
- Define owners for proposal preparation, technical review, signer coordination and post-execution verification.
- Attach transaction purpose, risk, linked code or config diff, simulation output and reviewer notes before approval.
- Keep emergency runbooks for pause, revoke, rotate, upgrade and communication decisions.
- Use templates so every signer sees the same context.
- Record final execution evidence and follow-up tasks.
- Use automation for preparation and reminders, not for bypassing signer accountability.
Implementation notes
The useful upgrade is not a bigger chat thread. It is a repeatable packet: what changes, why it changes, what can go wrong, who reviewed it, what evidence exists, and what the team does after execution.
Mistakes to avoid
- Approving transactions with only a short chat message.
- Relying on one operator to remember the context.
- Leaving emergency actions undefined.
- Mixing low-risk admin changes and high-risk treasury actions in the same review process.
- Not checking whether execution matched the approved intent.
How Nexuain helps
Nexuain helps Web3 teams turn Safe operations into documented runbooks, approval templates, dashboards and automation-assisted preparation while keeping human control explicit.
Nexuain practical implication
Safe operations improve when every transaction has purpose, payload, owner, review evidence and an escalation path before signatures start.
Source registry
- Safe 2026: source used to check Safe transaction tracking and signature collection. Nexuain interpretation: turn the reference into owners, evidence, permissions and human review.
- Safe 2026: source used to check multisig proposal and confirmation flows. Nexuain interpretation: turn the reference into owners, evidence, permissions and human review.
- CISA 2023: source used to check secure defaults and software accountability. Nexuain interpretation: turn the reference into owners, evidence, permissions and human review.
Related blog routes
Need help applying this to your launch or workflow?
Request a technical review and we will map the safest first step.